

keygraphhq / shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes real exploits to prove vulnerabilities before they reach production.
github.com/keygraphhq/shannonIndexed at 00e5645Up to date with upstream
About this codebase
135 files and 816 symbols in 2 modules, led by TypeScript (93 files) and Dockerfile (1).
Built from the index
Code health
This codebase scores 6.6 out of 10 for code health, which we rate fair. It also scores maintainability 8.1 and static performance 9.8 out of 10. The three are scored separately and never blended into one number. Risk is concentrated, as it usually is: 12 of 135 files are git hotspots, and they average 3.7 — which is where the fixes pay off most.
On the leaderboards:#26 of 37 TypeScript repos
Do next
1 thing worth doing this quarter.
Worth planning
Delete 12 unused symbols and files (183 lines)
Nothing in the graph reaches them, across 6 files; every reader and agent pays to skip them.
- symbols
- 12
- lines
- 183
- safe to delete
- Yes(inferred)
Small effort
Improve what Repowise can see
Add a test coverage report
Without one, Repowise cannot tell tested code from untested code, so every test-related action says “unknown”.
- line coverage
- Unknown, no report
Small effortReview the 138 proposed decisions
None is accepted yet, so nothing can drift from one and agents get no enforced guidance from them.
- proposed
- 138
- accepted
- 0
Medium effort
Use keygraphhq/shannon in your agent
Point Claude Code, Cursor, Codex or VS Code at this repository. Your agent gets the index this page is built from: cited answers, callers, history and health for any file.
https://api.repowise.dev/mcp/keygraphhq/shannonOne command, run anywhere. Adds the server to your local Claude Code config.
Docsclaude mcp add --transport http repowise https://api.repowise.dev/mcp/keygraphhq/shannon \ --header "Authorization: Bearer rw_live_xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx"
This repo is public, so anyone with a Repowise account and an API key can connect.
Try asking
- get_overview()
- get_answer("how is shannon put together?")
- get_why("why is shannon structured this way?")
Prefer local? pip install repowise && repowise init indexes your own checkout, no account needed.
Go deeper
- OverviewEverything the index found, what changed this week, commits and decisions.
- DocumentationModule-by-module documentation, written from the source.
- ArchitectureDependency graph, layers and third-party dependencies.
- Code healthEvery file's score, the findings behind it, tests and refactoring plans.
- CommitsEach commit's effect on code health, with agent provenance.
- ContributorsWho owns what, and where one person holds most of the knowledge.
- DecisionsArchitectural decisions mined from commits and pull requests.
- Ask this codebaseSign inGrounded answers over the indexed code.
Maintain this repo? Claim the page
Sign in with GitHub and we check that you are an admin or maintainer of keygraphhq/shannon. Then add a badge to the README that links readers here.
Use this repo from Claude or ChatGPT
Add this URL as a custom connector and sign in with repowise when asked. No API key to copy.
https://api.repowise.dev/mcp/keygraphhq/shannonFor maintainers
Add a badge to your README
Every badge is public, cached, and updates on its own after every index. Nothing to install.
Repowise badge
Links to this page, with no score on it. Adding it also re-indexes the repo every week.
[](https://repowise.dev/repo/keygraphhq/shannon?src=badge_wiki)Code health badge
The repo's health score out of 10, from the latest index.
[](https://repowise.dev/repo/keygraphhq/shannon?src=badge_health)Code health card
A larger card with the score, its change since the last index, and when it was measured. The HTML version follows the reader's light or dark theme.

[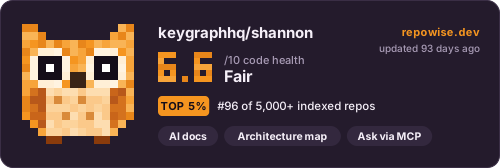](https://repowise.dev/repo/keygraphhq/shannon?src=badge_card)How keygraphhq/shannon works
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes real exploits to prove vulnerabilities before they reach production. This page is a map of the keygraphhq/shannon repository, written primarily in TypeScript, rebuilt from the source each time it is indexed. Repowise parses every symbol, computes a dependency graph, scores per-file code health from complexity, duplication, test coverage and churn, mines git history for hotspots and ownership, and lifts the architectural decisions into documentation you can read here or query through MCP.
The codebase has 135 files and 816 symbols in 2 modules, led by TypeScript, Dockerfile and JavaScript. Code health is 6.6 out of 10, rated fair.
Use the links above to open each view, or connect this repository to your agent for grounded answers inside Claude, Cursor, Codex or VS Code.