On this page
The best open source alternative to CodeScene is repowise, which scores every file's code health, ranks hotspots from git history, maps ownership and bus factor, and runs on your own machine. If you only need raw history data, code-maat or PyDriller are the open source building blocks; SonarQube Community Build covers static analysis but not git history.
The short list, as of October 2026:
- repowise: the packaged, self-hosted option. Code health, hotspots, ownership, change coupling and agent access in one tool.
- code-maat: Adam Tornhill's command line miner for version control history, the tool behind the hotspot method.
- PyDriller: a Python framework for mining git repositories into your own metrics.
- SonarQube Community Build: open source static analysis for bugs and code smells across many languages.
We build repowise, so weigh our entry accordingly. The measurements we publish about it, with their methods, are on the benchmarks page.
How we evaluated
We compared each tool on what teams use CodeScene for, using only each project's own documentation and pricing pages, fetched on 12 October 2026.
- Hotspots: does it combine change frequency with a measure of the code, to rank where work pays off?
- Ownership and knowledge risk: does it show who owns a file and how many people understand it?
- Code health score: does it score files directly, without you writing the scoring?
- Cost and openness: is the source open, and what do private repositories cost?
What CodeScene does well
CodeScene is a mature commercial platform that turns git history and code analysis into prioritized technical debt work. Its CodeHealth scoring, hotspot analysis, knowledge distribution views, delivery insights and automated pull request review are well regarded, and it supports more than 30 languages.
Pricing as of October 2026: Standard is €18 per active author per month, Pro is €27 and adds portfolio, team and delivery insights and coverage measurement, and Enterprise is custom and adds single sign-on, role-based access and a dedicated customer success manager. An active author is anyone who committed in the past three months. It runs on-premises or in the cloud, and open source projects get the Community Edition free.
The cost shows up on private code, where it scales with the number of active contributors. The source is closed, so the analysis cannot be inspected or extended. Those two points are why teams look for open source options.
Comparison table
| Tool | License | What it is | Hotspots | Ownership | Code health score | Agent access (MCP) |
|---|---|---|---|---|---|---|
| CodeScene | Commercial | Packaged platform | Yes | Yes | Yes | Yes (CodeHealth MCP Server) |
| repowise | AGPL-3.0 | Packaged, self-hosted | Yes | Yes | Yes | Yes (ten tools) |
| code-maat | GPL-3.0 | Command line miner | Churn and coupling data | Author counts and ownership | No | No |
| PyDriller | Apache-2.0 | Python library | You build it | You build it | No | No |
| SonarQube Community Build | Open source edition | Static analysis server | No | No | Quality gates, not a per-file health score | No |
Scroll the table sideways to see every column.
1. repowise
repowise is an open source (AGPL-3.0), self-hosted codebase intelligence tool that scores every source file from 1 to 10 and ranks what to fix first. It needs no LLM key for any of this. The analysis reads the parse tree, the dependency graph and git history during repowise init, and re-scores only changed files on repowise update (code health docs).
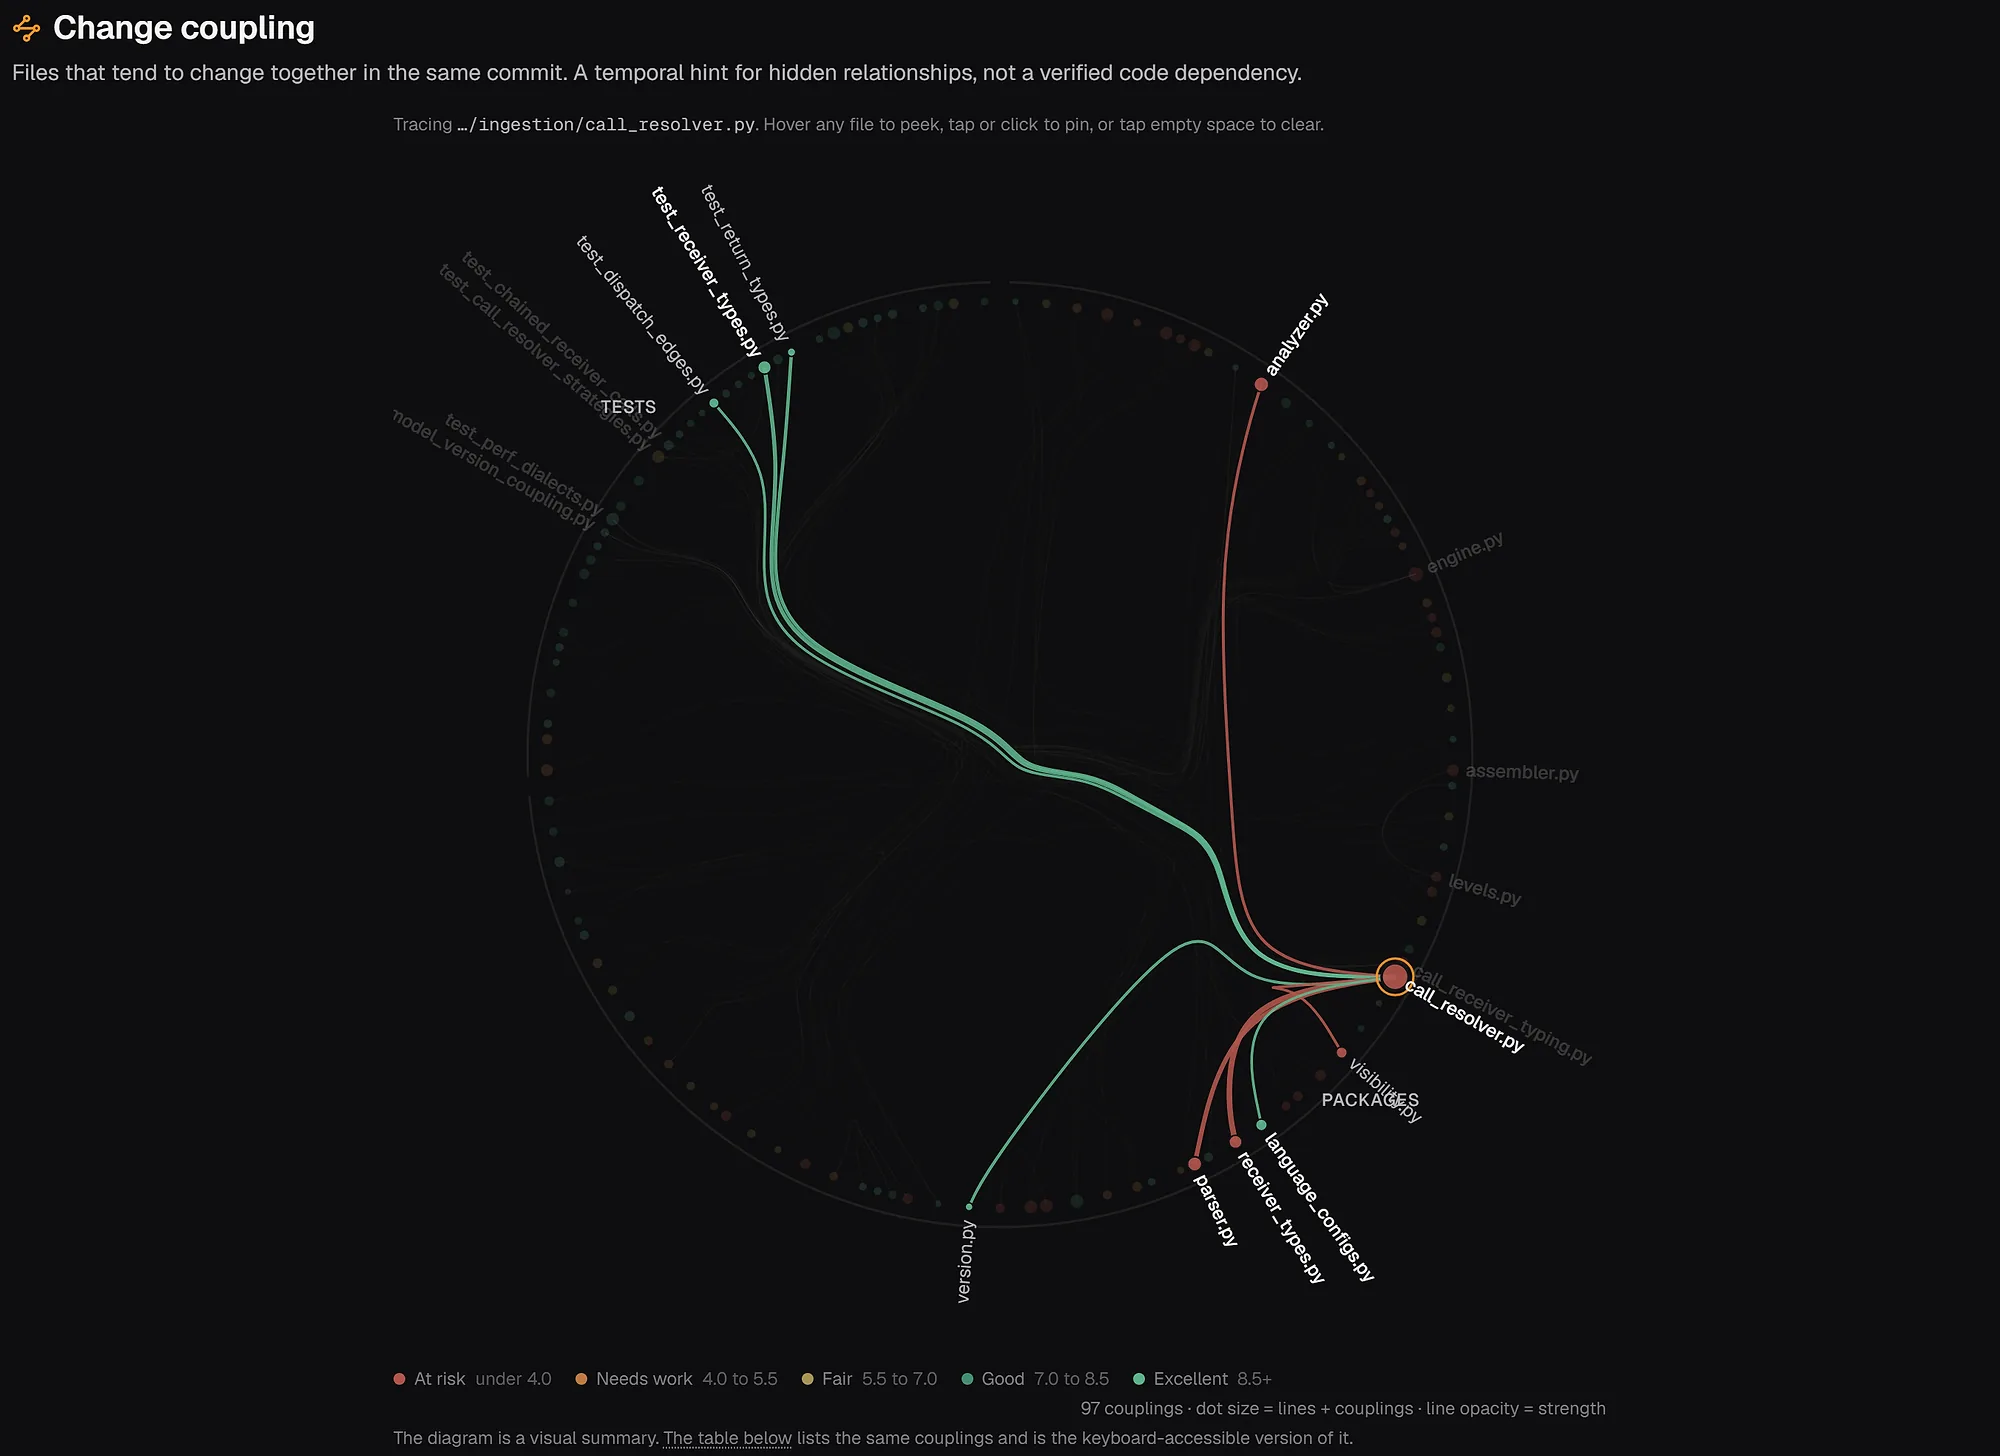
- Where it shines: the same decision space as CodeScene, in one install. Hotspots rank files by change frequency and prior bug fixes from full history. Ownership shows each file's main author, recent author and bus factor, and flags files still being edited after their owner has gone quiet. Change coupling lists files that move together in the same commits, which surfaces hidden dependencies a graph alone misses.
- Beyond CodeScene's core: a dependency graph across 28 languages parsed to a full syntax tree, dead code detection, an auto-generated wiki, and ten MCP tools so Claude Code, Cursor and other agents can ask for the same analysis.
repowise risk --fail-above-percentile 95scores a change against the repository's own history and can gate a CI job. - Pricing as of October 2026: the engine is free and open source. A hosted version has a free tier for public repositories, with private repositories on Pro.
- Pick it if you want CodeScene's hotspot, health and ownership views without a per-author bill, and want the same data available to coding agents.
pip install repowise
repowise init        # index: scores every file, mines git history
repowise health      # fix-first list, KPIs, lowest-scoring files
repowise risk        # defect risk for the current change
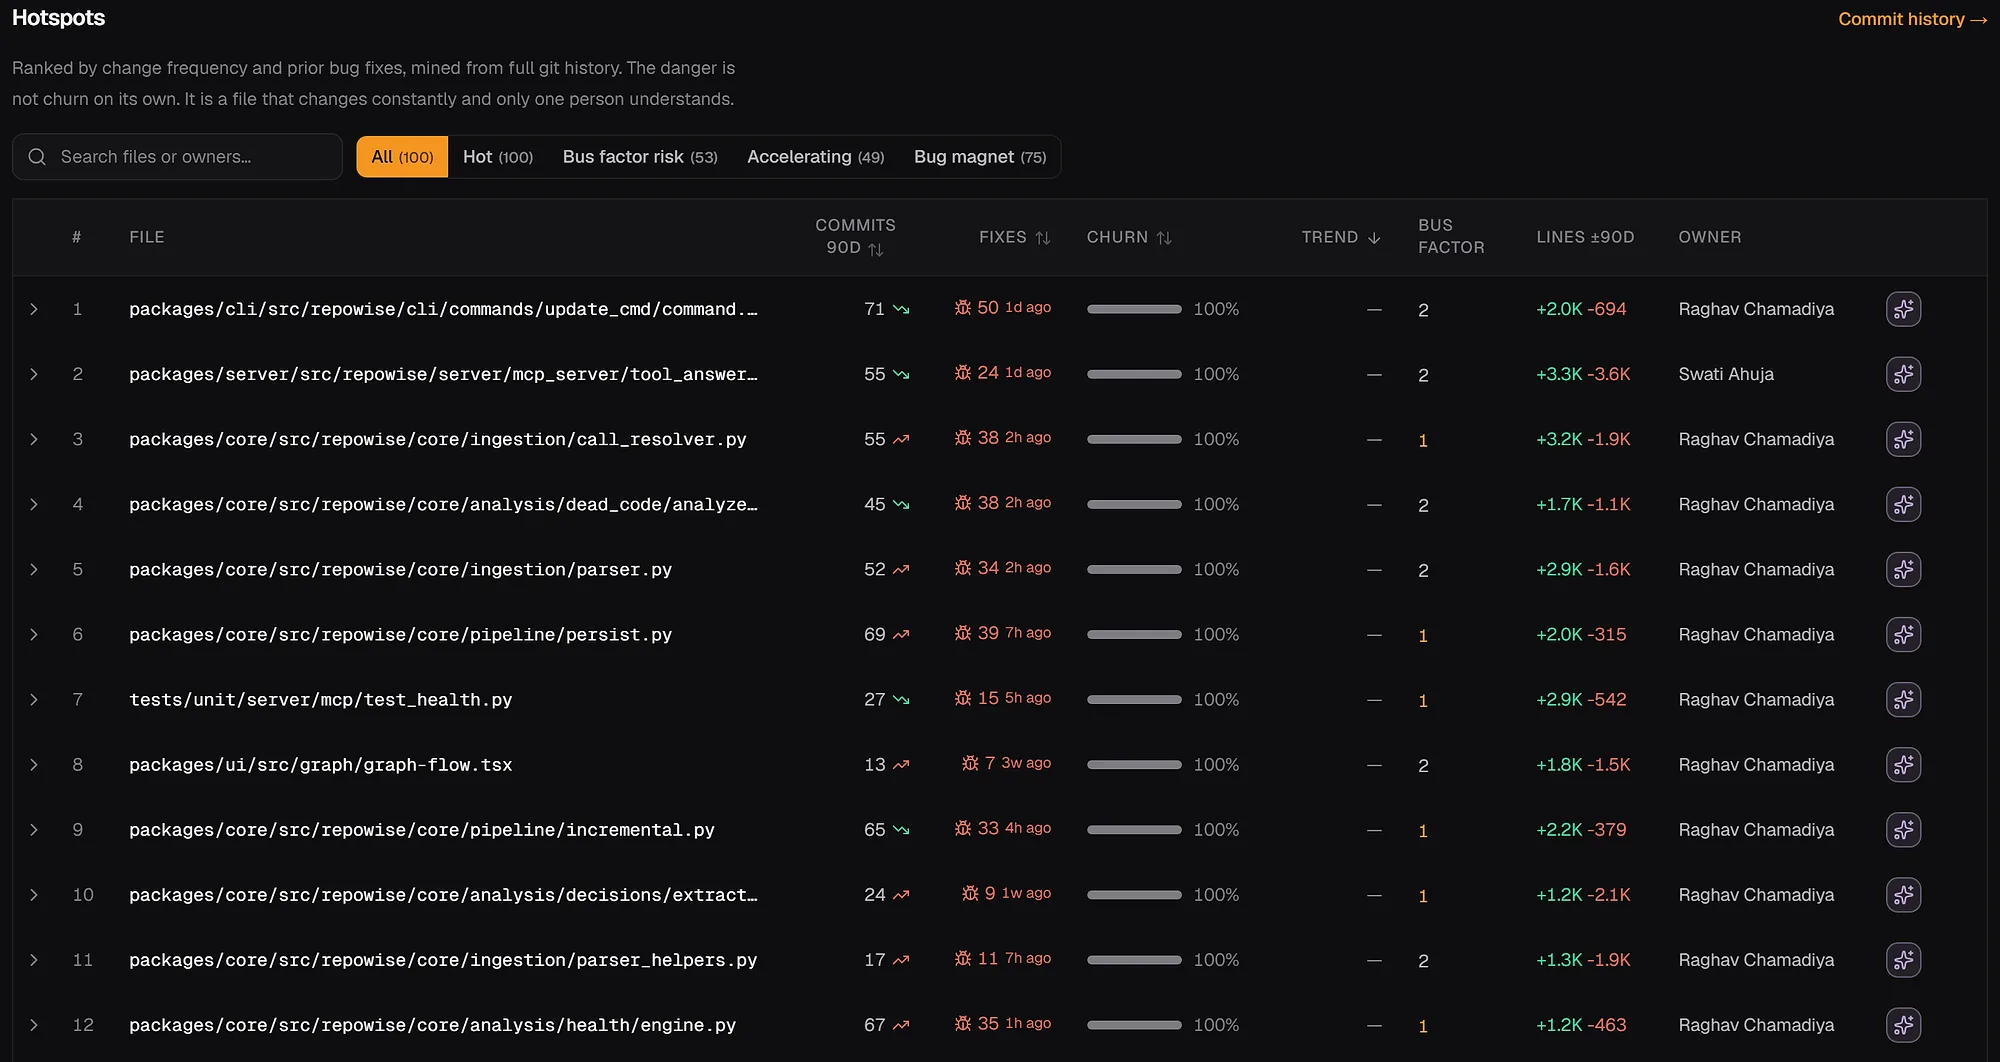
The hotspot view above is the repowise repository analyzing itself. The ranking is not churn alone: it weighs prior bug fixes and shows bus factor next to each file, because a file that changes constantly and that only one person understands is the real risk.
2. code-maat
code-maat is a GPL-3.0 command line tool that mines and analyzes version control data, and it is the original open source implementation of the hotspot method. It supports git, Mercurial, Subversion, Perforce and Team Foundation Server, and was written to accompany Adam Tornhill's books Your Code as a Crime Scene and Software Design X-Rays (repository).
- Where it shines: transparency and low ceremony. It reports author counts per module, logical coupling, code age, churn and ownership, as plain data you can pipe anywhere. It is a Clojure program that needs Java 8 or newer and ships as a JAR or Docker image.
- What you add yourself: a complexity measure to pair with churn, any visualization, a score and a place for the team to look at results.
- Pick it if you want to learn the method, or feed hotspot and coupling data into your own reporting.
3. PyDriller
PyDriller is an Apache-2.0 Python framework for extracting commits, developers, modified files and diffs from git repositories (repository, docs).
- Where it shines: it is the quickest way to build a custom metric if your team already writes Python. Churn, authorship concentration and rename-aware file history take a few dozen lines.
- What you add yourself: everything above the data: complexity, scoring, thresholds, storage and a UI.
- Pick it if you need a specific metric CodeScene does not offer, or a research pipeline across many repositories.
4. SonarQube Community Build
SonarQube Community Build is the free, open source edition of SonarQube, a static analysis server that checks code for bugs, vulnerabilities and code smells. SonarSource lists support for more than 40 languages and frameworks across its editions, with paid Team and Enterprise plans above the free build (Team starts at $34 a month as of October 2026).
- Where it shines: quality gates in CI and broad rule coverage. It answers "does this code have known problem patterns", which is a different question from "where does this team's history show risk".
- What it does not do: it is not a hotspot or ownership tool. It does not combine change history with code quality the way CodeScene and repowise do, so it complements the options above rather than replacing CodeScene.
- Pick it if you want rule-based quality gates alongside a history-based tool.
How to choose
Pick the tool by what you are replacing, not by feature count.
- Replacing CodeScene's hotspots, health scores and ownership, self-hosted: repowise.
- Want agents to use the same signals: repowise, which exposes them over MCP.
- Learning the method or feeding a data pipeline: code-maat for ready-made analyses, PyDriller for custom ones.
- Want rule-based static analysis in CI: SonarQube Community Build, next to a history-based tool.
- Need a vendor with support, single sign-on and delivery analytics: CodeScene is built for that, and is free for open source projects.
To evaluate fairly, index one repository with repowise, then compare its hotspot list to the one your team already trusts. Our CodeScene comparison goes through the feature differences, and git intelligence covers the history-based analysis in depth.
FAQ
- Is there an open source alternative to CodeScene?
- Yes. repowise is open source under AGPL-3.0 and covers code health scoring, hotspots, ownership and change coupling in one self-hosted tool. code-maat (GPL-3.0) and PyDriller (Apache-2.0) are open source libraries for mining git history that you build metrics on.
- Is CodeScene free?
- CodeScene is free for open source projects through its Community Edition, and offers a free trial for paid plans. For private repositories it costs €18 (Standard) or €27 (Pro) per active author per month as of October 2026, which is a commercial license, not open source.
- Can open source tools replace CodeScene hotspots?
- Yes. A hotspot is a file with high change frequency and high complexity or bug history. repowise computes it for you from full git history, and code-maat or PyDriller provide the raw data if you want to build the ranking yourself.
- Is repowise really open source?
- Yes. The engine is published under the AGPL-3.0 license, a copyleft license that requires source availability for networked use. Review the obligations with your legal team if you plan to modify it and offer it as a service.
- Does SonarQube replace CodeScene?
- Not on its own. SonarQube Community Build checks code against rules for bugs and smells, while CodeScene reads git history to find hotspots and knowledge risk. Many teams run a static analyzer and a history-based tool side by side.